SONARQUBE

Code confidence for the agentic software factory

SonarQube delivers independent, zero-trust, multilayered verification and governance for every change, whether a developer or an AI wrote it.

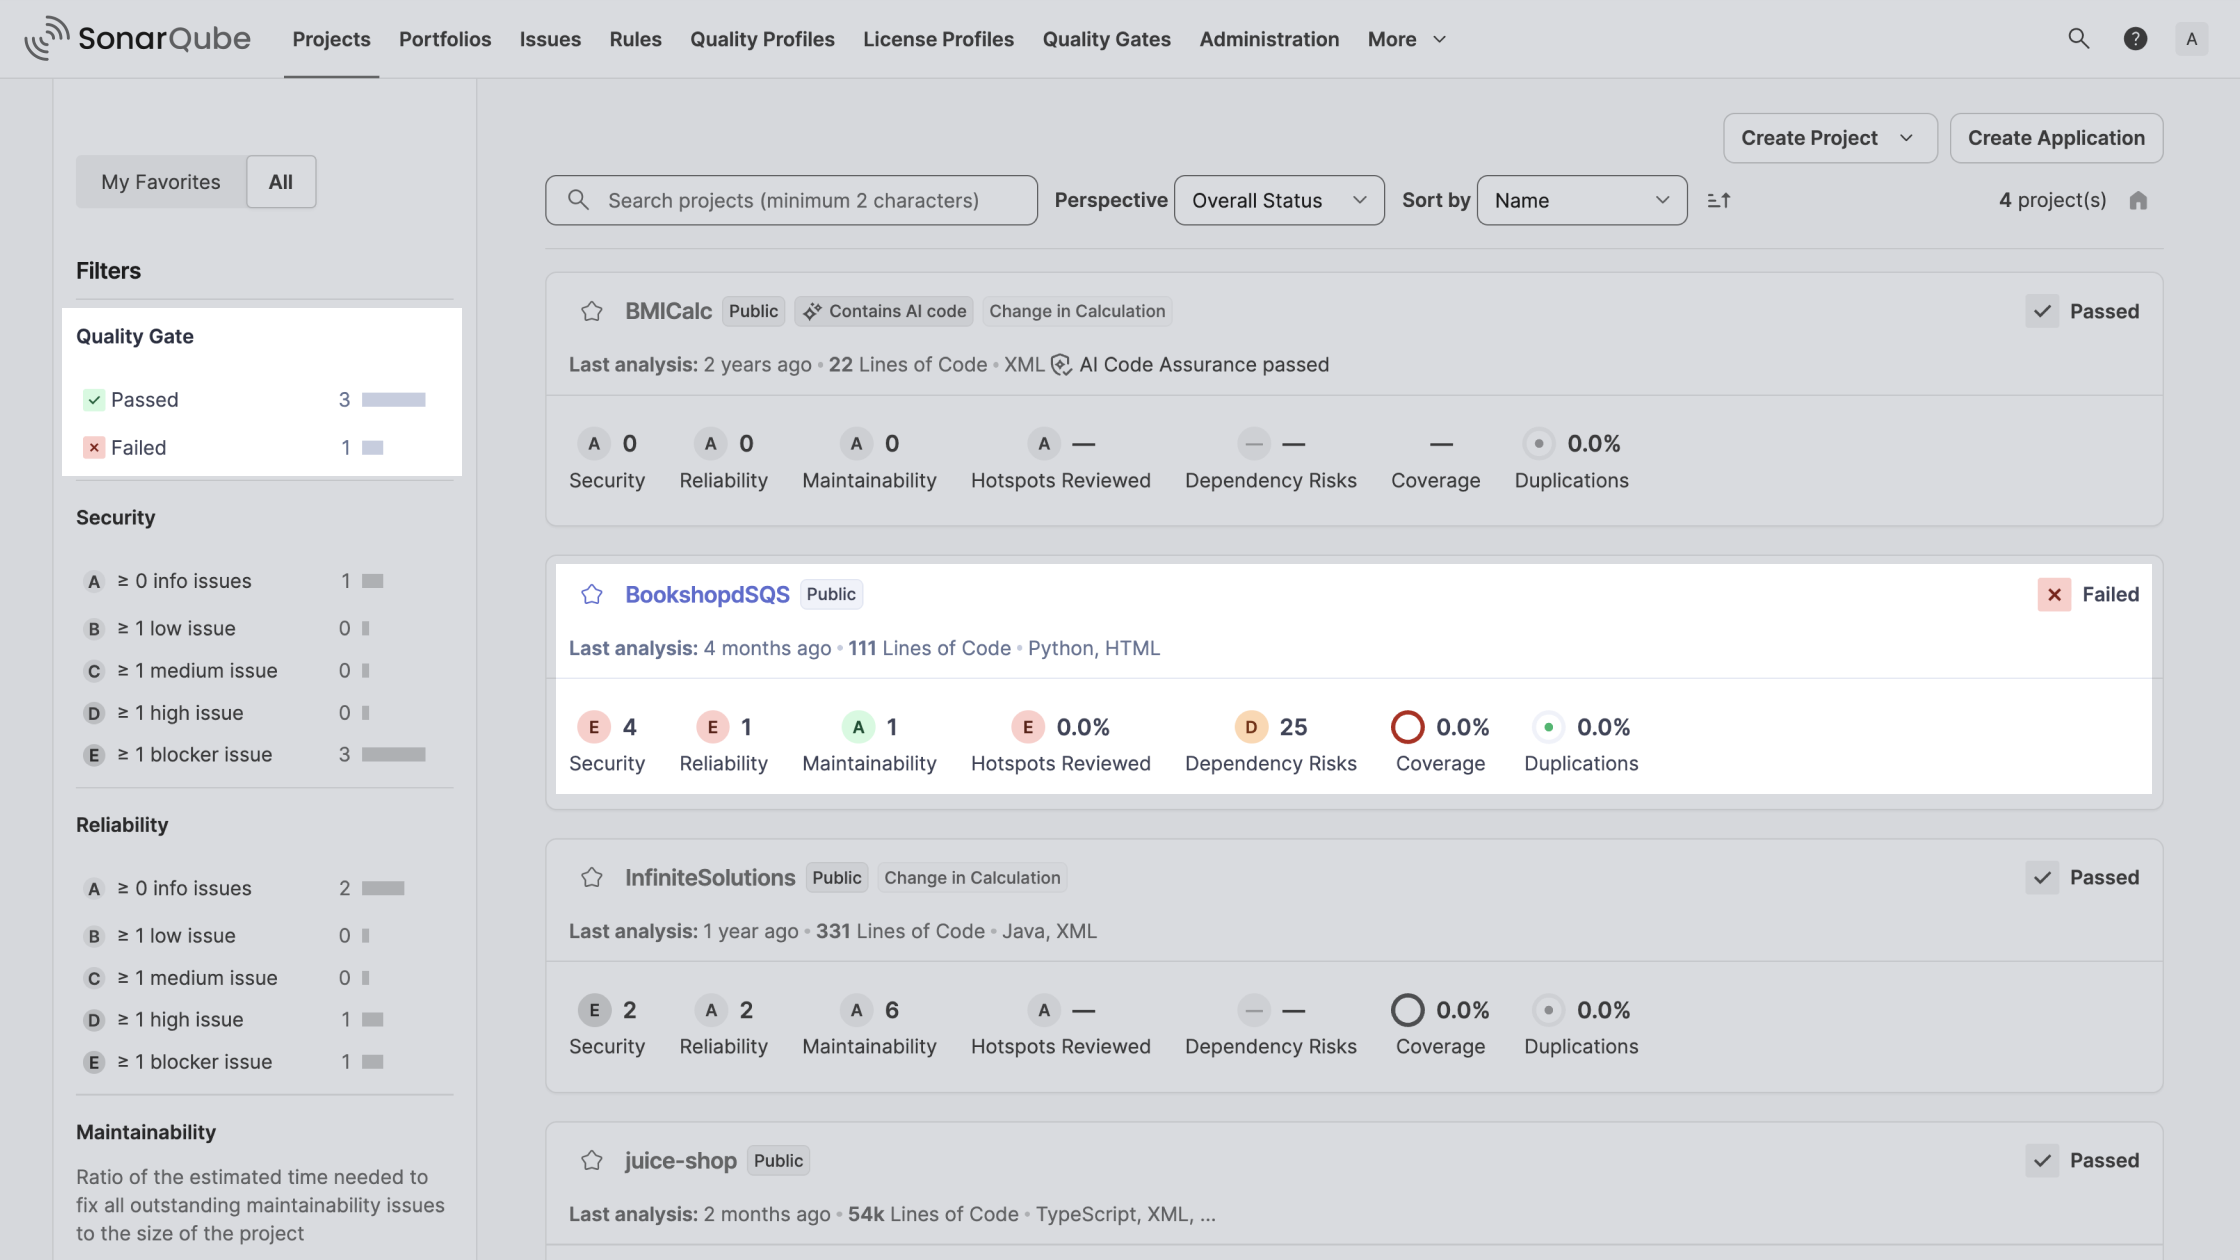
SonarQube Server dashboard showing code quality and security results
Trusted by over 7M developers and 75% of the Fortune 100
Mercedes Benz
Nvidia
Santander
BUILD CONFIDENCE

The four components of code confidence

Here’s how SonarQube brings confidence to agentic software development across every code change, from generation through review and audit.

Intent

Goals and standards, clearly specified

Architects and tech leads set the standards: quality profiles, intended architecture, and security policies. SonarQube turns them into one definition of “right” that every developer and coding agent works to.

Guiderails

That guide and govern

SonarQube plugs into your IDEs and coding agents via plugins, CLI, and MCP, so the standards you set apply wherever code is written, by a person or an agent.

Verification

Thorough, independent, actionable

Every pull request gets a zero-trust, multilayered review that finds reliability, security, and maintainability issues and fixes them before the change ships.

Evidence

Consistent, auditable, repeatable

Quality gates decide what merges and record every check. Each result is time-stamped and tied to the commit, so you can show auditors why a change shipped.

Cloud and Server

Same verification. Run it where your code lives.

Verify AI and human code the same way, with Sonar hosting it or inside your own perimeter. Pick the deployment that fits your security and compliance needs.

SaaS

SonarQube Cloud: fully managed by Sonar

Verification that runs and maintains itself, so your team spends its time on code, not infrastructure.

  • Start verifying code today. Connect a repo and the quality gate is live the same day, with no servers to run.
  • Stay current without upgrade projects. New rules and AI-code checks arrive automatically, so your gate never lags the code being written.
  • Keep your team shipping. Sonar runs and maintains it.
Best forTeams that want verification live this week
MaintenanceHandled by Sonar
Self-Hosted

SonarQube Server: self-managed inside your perimeter

The same verification on infrastructure you control, built for teams that must keep code and findings in-house.

  • Keep code and findings inside your perimeter. Runs on your infrastructure, including air-gapped, so residency and privacy rules are met by design.
  • Fit verification to your enterprise. Custom configuration and integrations match how your org already governs releases.
  • Prove every merge decision to auditors. The same time-stamped, traceable quality-gate evidence, on your terms.
Best forRegulated teams that must self-host
MaintenanceYou control upgrades and infrastructure
In both

Same systematic code analysis, same quality gates, same evidence.

Capabilities

SonarQube capabilities

Apply one standard for code quality, security, and governance to every developer and every coding agent.

Catch bugs and debt before they merge.

Learn more

Find vulnerabilities while the code is still being written.

Learn more

Know what's in your software, and what it exposes.

Learn more

Define your architecture. See where code drifts from it.

Learn more

Works where your team already works.

See all integrations

Governance and reporting

Learn more
Security Capabilities

Developer-led code security

Empower developers with real-time, actionable guidance to detect and fix vulnerabilities as code is written and reviewed, directly in their workflow.

Static Application Security Testing (SAST)

Our SAST engine automatically finds critical vulnerabilities in your development workflow, stopping them before they reach production.

  • Detect critical vulnerabilities: Identifies OWASP Top 10 and beyond — injection, authentication flaws, XSS, and more — with high precision and low false-positive rates.
  • Broad language support: Covers the most popular programming languages, including Java, JavaScript, Python, C++, C#, and many more.
  • Seamless workflow integration: Get immediate feedback directly in your IDE and CI/CD pipeline without context switching.
  • Rapid remediation: Resolve issues faster with clear guidance and AI-powered CodeFix suggestions.
  • Customizable policies: Enforce your organization’s specific security standards by creating custom detection rules.
Learn more about SAST

Taint analysis

Our taint analysis engine tracks data flow to find and stop critical injection vulnerabilities.

  • Find critical injection flaws: Accurately detects a wide range of vulnerabilities, including SQL injection, Cross-site scripting (XSS), SSRF, and more.
  • Minimize false positives: Utilizes sophisticated cross-file and cross-function analysis to deliver highly accurate, actionable results.
  • Framework-aware intelligence: Understands the native security controls in popular frameworks, leading to smarter and more relevant findings.
Explore taint analysis

Secrets detection

SonarQube detects leaked code secrets throughout your development workflow, identifying them directly in the IDE and within your CI/CD pipeline.

  • Comprehensive coverage: Finds API keys, passwords, and security tokens with hundreds of patterns covering all popular cloud providers and services.
  • High-fidelity scanning: Goes beyond basic pattern matching, using a powerful combination of regular expressions and semantic analysis to minimize false positives.
  • Customizable rules: Easily define your own patterns to detect organization-specific secrets for internal applications and private services in the Enterprise Edition.
  • Shift-left detection: Get immediate feedback directly in your IDE, allowing you to remove secrets before they are ever committed to the repository.
Learn more about secrets detection

Infrastructure as Code (IaC) scanning

Find and fix Infrastructure as Code (IaC) misconfigurations before they reach production to secure your cloud.

  • Broad IaC coverage: Scans popular tools including Terraform, CloudFormation, Kubernetes, Azure Resource Manager (ARM), and Ansible.
  • Identify key risks: Catches critical security issues like overly permissive access, publicly exposed services, and insecure defaults.
  • Actionable remediation: Get clear, precise results with step-by-step guidance to help you fix misconfigurations quickly and efficiently.
Learn about IaC scanning

Advanced SAST

Advanced SAST helps identify deeper and more complex vulnerabilities due to the interaction of your application code with third-party (open-source) code.

  • Dependency-aware scanning: Traces data flows not just through your application, but deep into the third-party libraries it relies on.
  • Uncover hidden vulnerabilities: Cross-file taint analysis that goes deep into third-party libraries for detecting hard to find vulnerabilities.
  • Effortless and fast: Runs automatically with zero configuration and no performance overhead, delivering quick and accurate results.
  • Language support: Currently available for Java, C#, JavaScript, and TypeScript.
Discover Advanced SAST

Software Composition Analysis (SCA)

Secure your open-source dependencies by finding vulnerabilities, managing licenses, and inventorying your software supply chain.

  • Vulnerability detection: Automatically find, track, and prioritize known vulnerabilities (CVEs) within your third-party components.
  • License compliance: Check for and flag incompatible or unapproved licenses in your dependencies to avoid legal and compliance risks.
  • Software bill of materials (SBOM): Generate a complete and accurate inventory of every component in your software for essential transparency and security audits.
Learn more about SCA
Sonarqube

Frequently asked questions

What is SonarQube?

How does SonarQube verify AI-generated code?

How do coding agents work with SonarQube?

What is Sonar Vortex?

What is SonarQube Hunter Agent?

What is SonarQube Remediation Agent?

Should I choose SonarQube Cloud or Server?

Is SonarQube a SAST tool?

How does SonarQube keep standards consistent across teams?

How does SonarQube work with pull requests and CI/CD?

Is there a free option?

Which programming languages does SonarQube support?

What reports does SonarQube provide for audits?

What is SonarQube AI CodeFix, and how do I enable it?

Build code confidence into your software factory